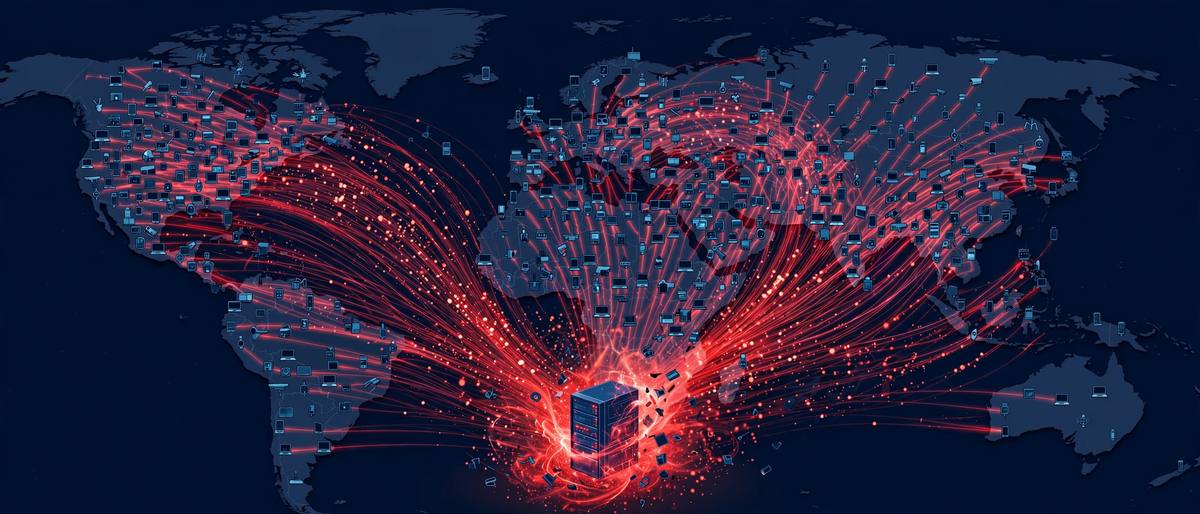
A DDoS attack — distributed denial of service — is an attempt to make a website or online service unavailable by flooding it with more traffic than it can handle. When people ask for a DDoS attack explained simply, the best analogy is a traffic jam deliberately created around a single shop: so many fake customers block the entrance that real customers can’t get in. The site isn’t necessarily hacked; it’s just overwhelmed.
DDoS attacks are among the most visible cyberattacks because their effects are public: websites go down, games lag unbearably, services display error pages. They’re used for extortion, competitive sabotage, hacktivist protests, and sometimes just chaos. Understanding how they work helps you interpret outages — and, if you run a website, prepare for them.
This guide explains the mechanics of DDoS attacks, the botnets that power them, the main attack types, why attackers launch them, and the defenses that keep sites online. You’ll also learn what to do as an ordinary user when a favorite service goes dark.
- How a DDoS Attack Works
- Botnets: The Engine of DDoS
- Main Types of DDoS Attacks
- Why Attackers Launch DDoS Attacks
- How Websites Defend Against DDoS
- DDoS as a User: What You Can Do
How a DDoS Attack Works
Every server has finite capacity: bandwidth, processing power, memory. A DDoS attack exhausts one of these by coordinating thousands or millions of compromised devices to send requests simultaneously. Legitimate traffic can’t compete with the flood, so the service slows to a crawl or collapses entirely. The “distributed” part is key — traffic comes from everywhere at once, making it hard to simply block one source.
Attackers don’t need to break in to cause damage. Unlike hacking, which seeks unauthorized access, DDoS seeks unavailability. That’s what makes it brutally simple: no vulnerability required, just volume. Modern attacks regularly exceed a terabit per second — far beyond what most organizations can absorb alone.
The distributed nature also complicates response. Blocking attacking IP addresses is whack-a-mole when millions of devices participate, many of them innocent people’s compromised cameras and routers. Effective defense requires absorbing and filtering the flood upstream, before it reaches the target — which is why mitigation is typically a specialized service rather than a DIY project.
Botnets: The Engine of DDoS
Behind nearly every large DDoS attack is a botnet: a network of compromised devices controlled by the attacker. These aren’t just computers — modern botnets heavily recruit Internet of Things devices: security cameras, routers, DVRs, and smart gadgets with default passwords and unpatched firmware. The Mirai botnet famously demonstrated this by enslaving hundreds of thousands of IoT devices.
Botnets are also a business. They’re rented by the hour on illicit markets, meaning anyone with modest funds can launch a substantial attack without technical skill. This commoditization is why DDoS has become a routine tool for extortion and harassment rather than a rare sophisticated operation.
Here’s the uncomfortable part: your devices could be participants. An unpatched router or camera with a default password can be conscripted without any visible symptom. Keeping firmware updated and changing default credentials isn’t just self-protection — it’s civic hygiene that shrinks the botnets threatening everyone. If a site you run ever faces an attack, a content delivery network (CDN) is one of the primary defenses, absorbing floods across its distributed edge.
Main Types of DDoS Attacks
DDoS attacks target different layers. Volumetric attacks flood the network pipe with sheer traffic — UDP floods and amplified DNS or NTP reflection attacks that trick third-party servers into bombarding the victim. These are the terabit-scale headline attacks, fought with bandwidth and filtering capacity.
Protocol attacks exploit weaknesses in network protocols themselves: SYN floods that exhaust connection tables, or malformed packets that crash fragile systems. They’re measured in packets per second rather than bits, and they target the machinery of networking rather than raw capacity.
Application-layer attacks are the subtlest: they mimic legitimate requests — repeatedly loading a search page or triggering expensive database queries — to exhaust the server’s processing power. Because the traffic looks normal, these are hardest to filter and can succeed with relatively modest volume. Defending requires understanding normal traffic patterns, which is one reason site owners should secure their WordPress websites comprehensively rather than relying on any single protection.
Why Attackers Launch DDoS Attacks
Motivations vary widely. Extortion is common: attackers threaten an attack unless paid, or launch a short demonstration attack to prove capability. Competitors have hired DDoS services against rival gaming servers, gambling sites, and e-commerce stores. Hacktivist groups use DDoS as digital protest against organizations they oppose.
Sometimes DDoS is a smokescreen: while defenders scramble to restore service, attackers quietly breach systems or steal data amid the chaos. And sometimes the motive is simply malice or boredom — gaming communities and streamers are frequent targets of petty attacks. Geopolitical conflicts have also featured DDoS against government and media sites.
Understanding motivation matters for response: an extortion attempt should be reported to law enforcement rather than paid (payment invites repeat attacks), while hacktivist campaigns typically subside. In all cases, having mitigation in place beforehand beats scrambling during an outage.
How Websites Defend Against DDoS
Modern DDoS defense is layered. CDNs distribute content across global edge servers, absorbing volumetric attacks across massive aggregate capacity. Dedicated DDoS mitigation services scrub traffic — analyzing it in real time, dropping malicious flows, and passing clean traffic through. Rate limiting and web application firewalls blunt application-layer attacks.
Architectural choices help too: over-provisioned capacity, anycast routing that spreads attacks across locations, and caching that reduces the work each request demands. For smaller sites, a reputable CDN with built-in DDoS protection is the most cost-effective defense — it’s included rather than enterprise-priced.
Preparation beats reaction: know your hosting provider’s DDoS policies, have a communication plan for outage announcements, and monitor traffic baselines so anomalies surface quickly. Most small sites will never face a major attack, but the same CDN that speeds up your site (see our guide on testing your internet speed to understand the performance side) also provides this protection as a side benefit.
DDoS as a User: What You Can Do
When a service you use goes down, a DDoS attack is one possible cause — but so are many mundane failures. Check the service’s status page or official social accounts before assuming attack; providers usually communicate during major incidents. Avoid hammering refresh, which adds load, and be patient — most attacks are mitigated within hours.
Be skeptical of claims during outages: attackers sometimes publicize attacks for notoriety, while unrelated parties spread misinformation. Stick to official channels. And use the experience as a reminder to keep your own devices out of botnets: updated firmware, changed default passwords, and retired devices properly wiped.
DDoS illustrates a broader security truth: availability is part of security, and defending it requires planning before the crisis. For authoritative technical guidance, CISA’s resources at https://www.cisa.gov/ cover DDoS preparation and response for organizations of all sizes.